The 4-Perimeter Framework
AI agents read your data and take actions on behalf of users. Without access control at each step, they can reach data and perform actions the user behind them isn't allowed to.
The Key: Fine-grained authorization (FGA)
FGA checks every access against policy, so users, and the AI agents acting on their behalf, can reach and act on only the data they're allowed to. That limits the damage from misuse, prompt injection, and sensitive data exposure.
The Four-Perimeter Framework applies FGA at four points in an AI interaction, from the prompt to the final response.
Prompt Filtering
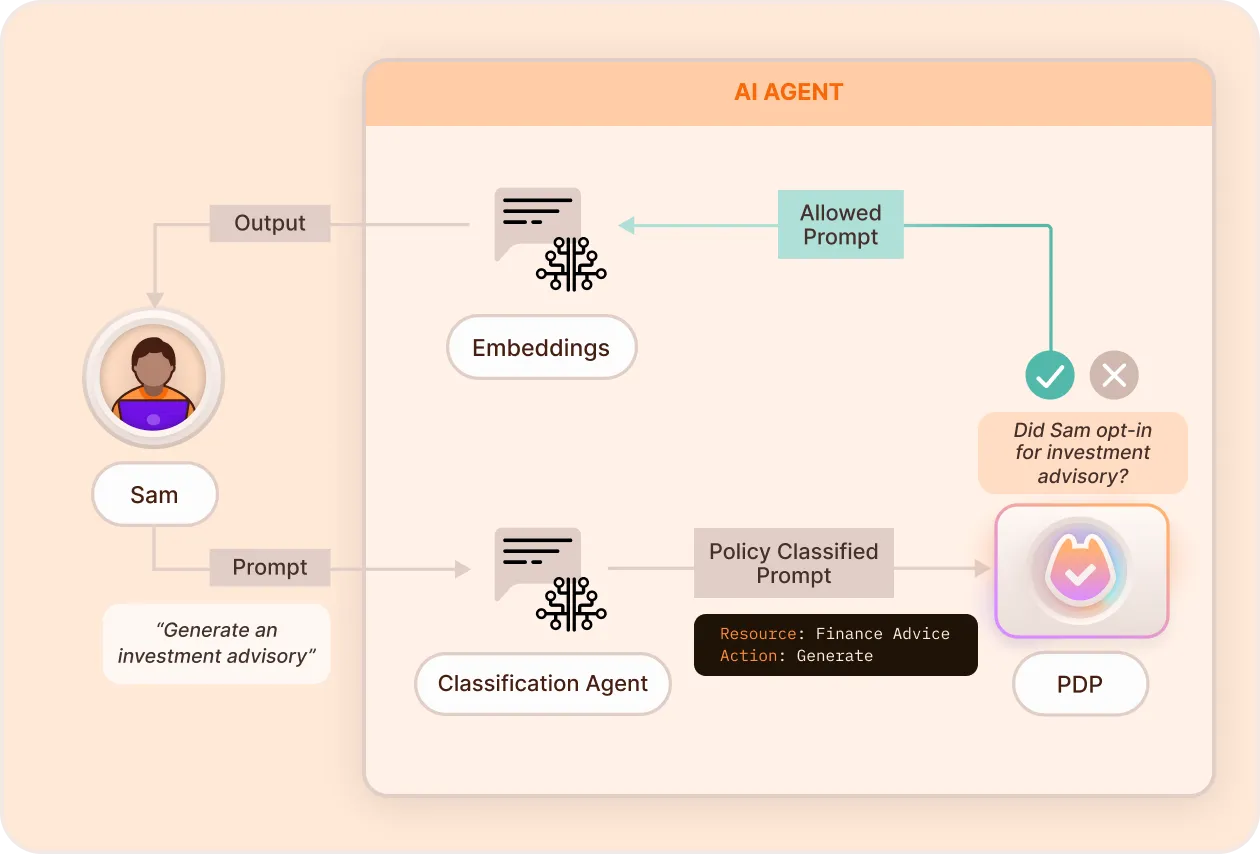
Prompt Filtering stops unauthorized input before it reaches the AI model. Policy is evaluated before the LLM receives the prompt, which helps mitigate prompt injection, data exfiltration, and overreach.
Key Features
- AI-Driven Intent Classification: Utilize OpenAI's language models to understand the user's intent behind natural language prompts.
- Dynamic Access Enforcement: Apply permissions in real-time based on the classified intent and user attributes before prompts reach the AI model.
- Flexible Access Patterns: Handle complex attribute matching and simple validations without hardcoded rules.
- Natural Language Understanding: Allow users to interact using plain English, with the system inferring necessary details.
Further Reading
- Guide: Prompt Filtering with OpenAI: Using GPT for GPT Access Control
- GitHub Repo: permit-prompt-filtering
RAG Data Protection
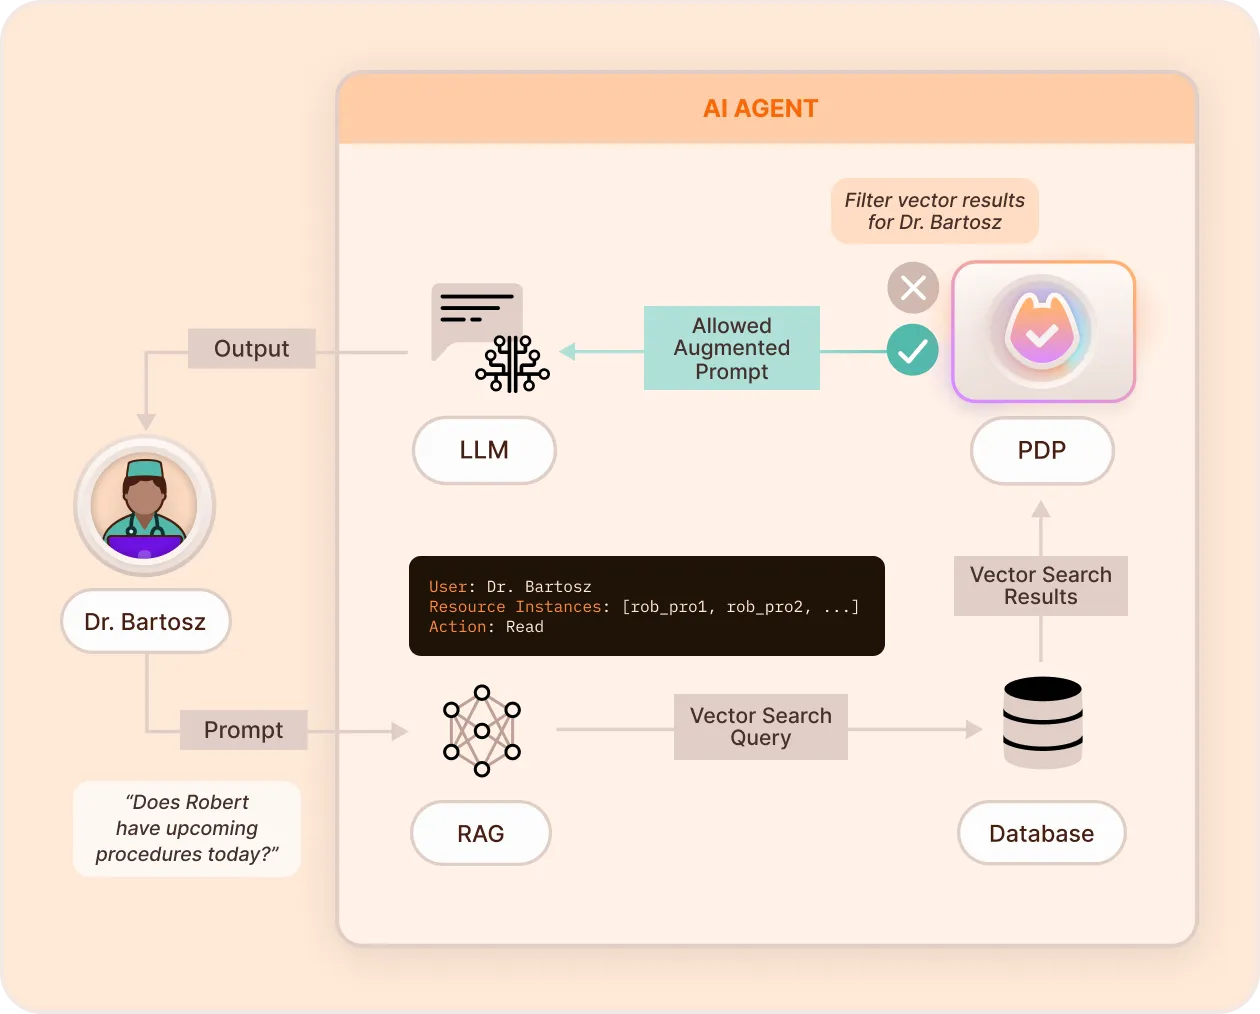
RAG Data Protection filters what the retrieval-augmented generation (RAG) layer can retrieve from knowledge bases, documents, and vector stores, so the model sees only data the user is authorized to access.
Key Features & Benefits
- Granular Access Control: define who can retrieve what from vector databases and knowledge bases.
- Fine-Grained Filtering: apply attribute-based access control (ABAC) to RAG queries.
- Pre-Query & Post-Query Filtering: restrict data access before retrieval, or filter results after retrieval.
- Framework Integration: use Permit's RAG security components in chain and agent frameworks to apply FGA to data retrieval.
Further Reading
- Guide: Building AI Applications Using RAG and FGA
- GitHub Repo: permit-mongodb-secure-rag
Secure External Access
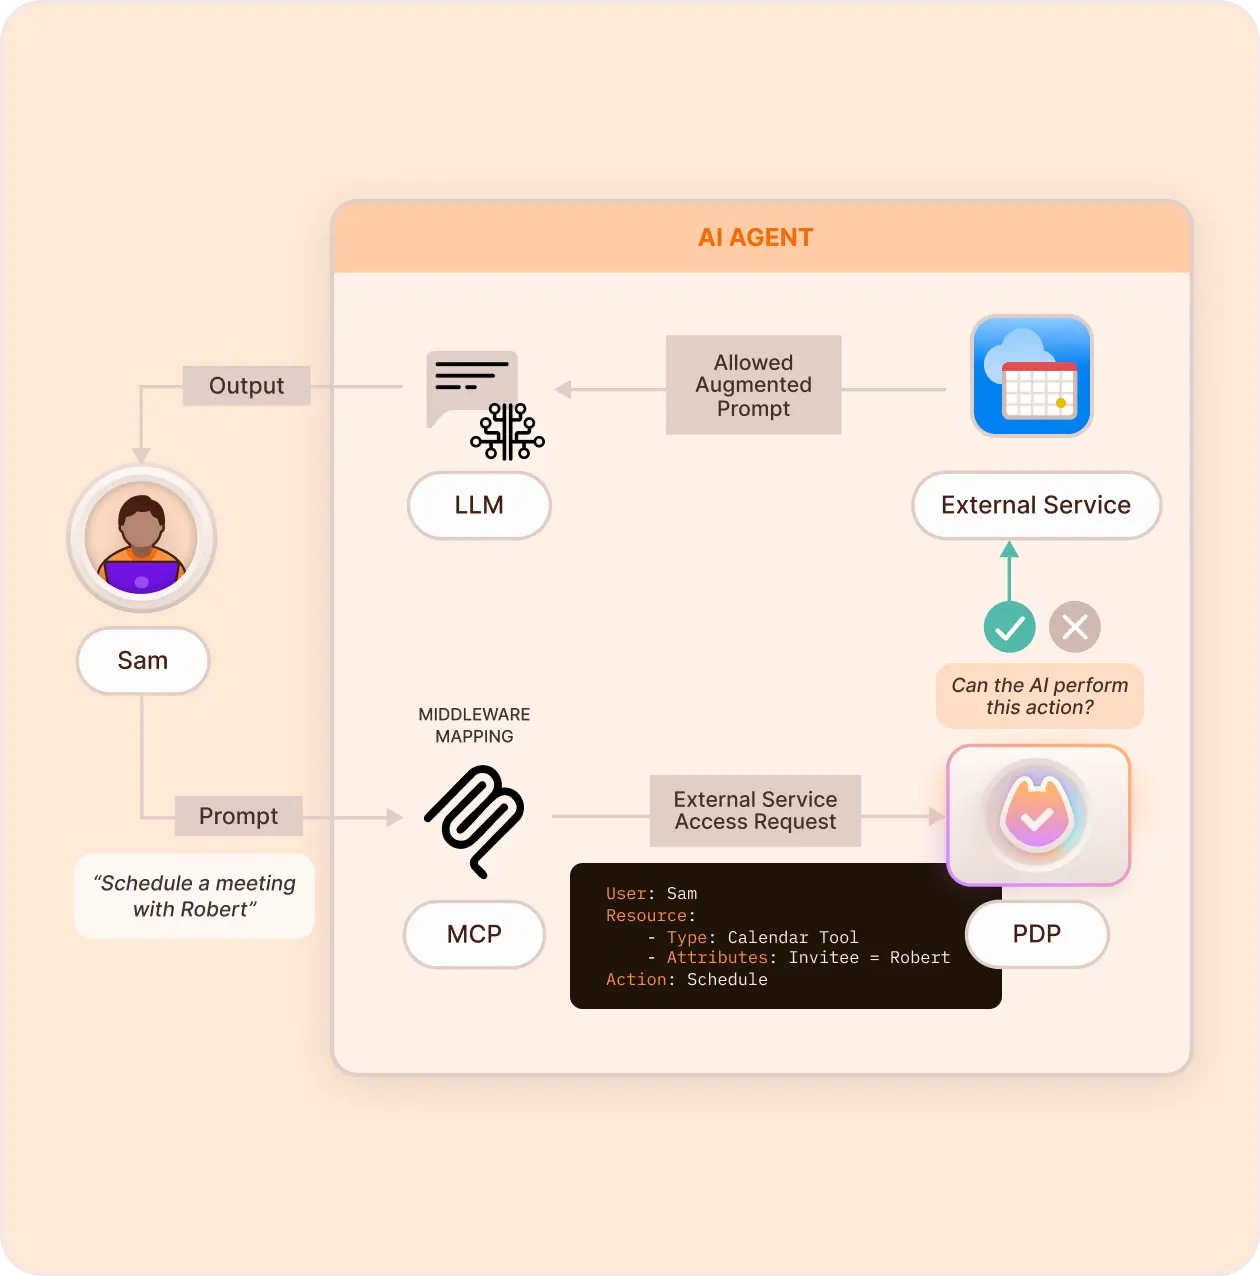
Secure External Access applies policy when AI agents act in the real world, through API calls, transactions, or external services, so each action is tied to an identity and limited to what that identity may do.
Key Features & Benefits
- Enforce Identity-Based Permissions - Assign machine identities to AI agents to track and manage their access to external tools and resources.
- Define Permitted Actions - Specify which API calls, transactions, and operations are AI-authorized.
- User-Approved Transactions - Require human approval for critical actions (e.g., purchases, bookings, or account changes).
- Approval Flow / Access Request APIs - Enable dynamic approvals and access requests through APIs and embeddable no-code interfaces.
- Access on Behalf - Create traceable, auditable policies for actions made on behalf of human/AI users, with full decision-making chain visibility.
Further Reading
- Guide: Delegating AI Permissions to Human Users with Access Request MCP
- GitHub Repo: permit-mcp
Response Enforcement
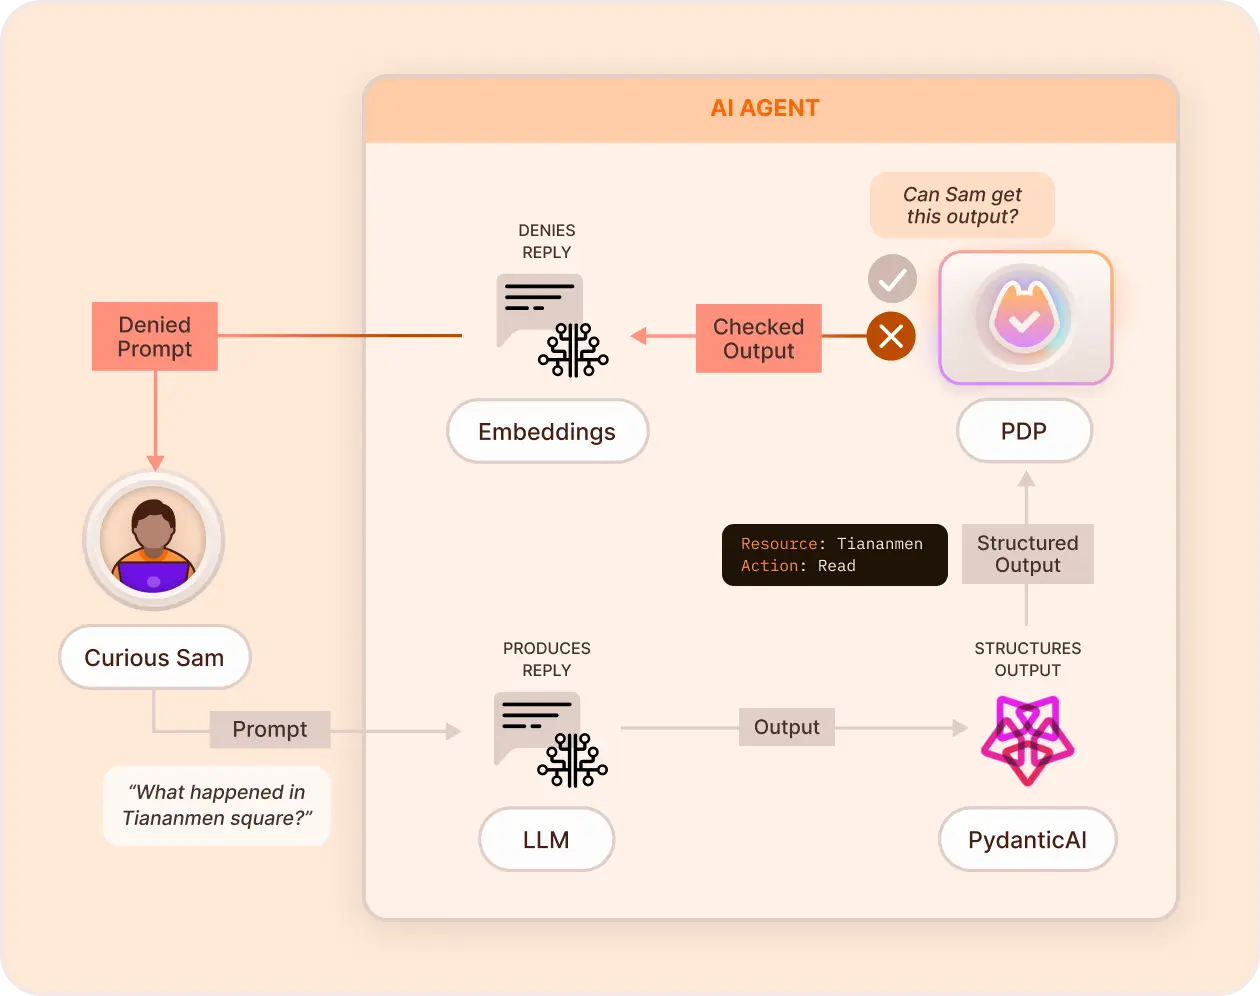
Response Enforcement applies policy to the AI model's output before the user sees it, so responses don't expose data the user isn't allowed to see.
Key Features & Benefits
- Output Filtering - Apply content moderation rules to remove sensitive or inappropriate information before response delivery.
- Compliance Policies - Use classification and access control to ensure AI-generated responses align with pre-determined policies.
- Custom Role-Based Output Control - Define what different user roles can and cannot see in AI-generated responses.
Further Reading
- Guide: Response Enforcement with PydanticAI
- GitHub Repo: Permit-PydanticAI